On Monday night we rented a suite at the Delta Center, filled it with about twenty IT leaders from Utah construction companies, credit unions, medical practices, and professional-services firms, and watched the Mammoth beat the Penguins. Somewhere between the traffic and the second period, we also had the shortest cyber insurance conversation most of them had ever had.
Here’s what we talked about, for the people who couldn’t make it.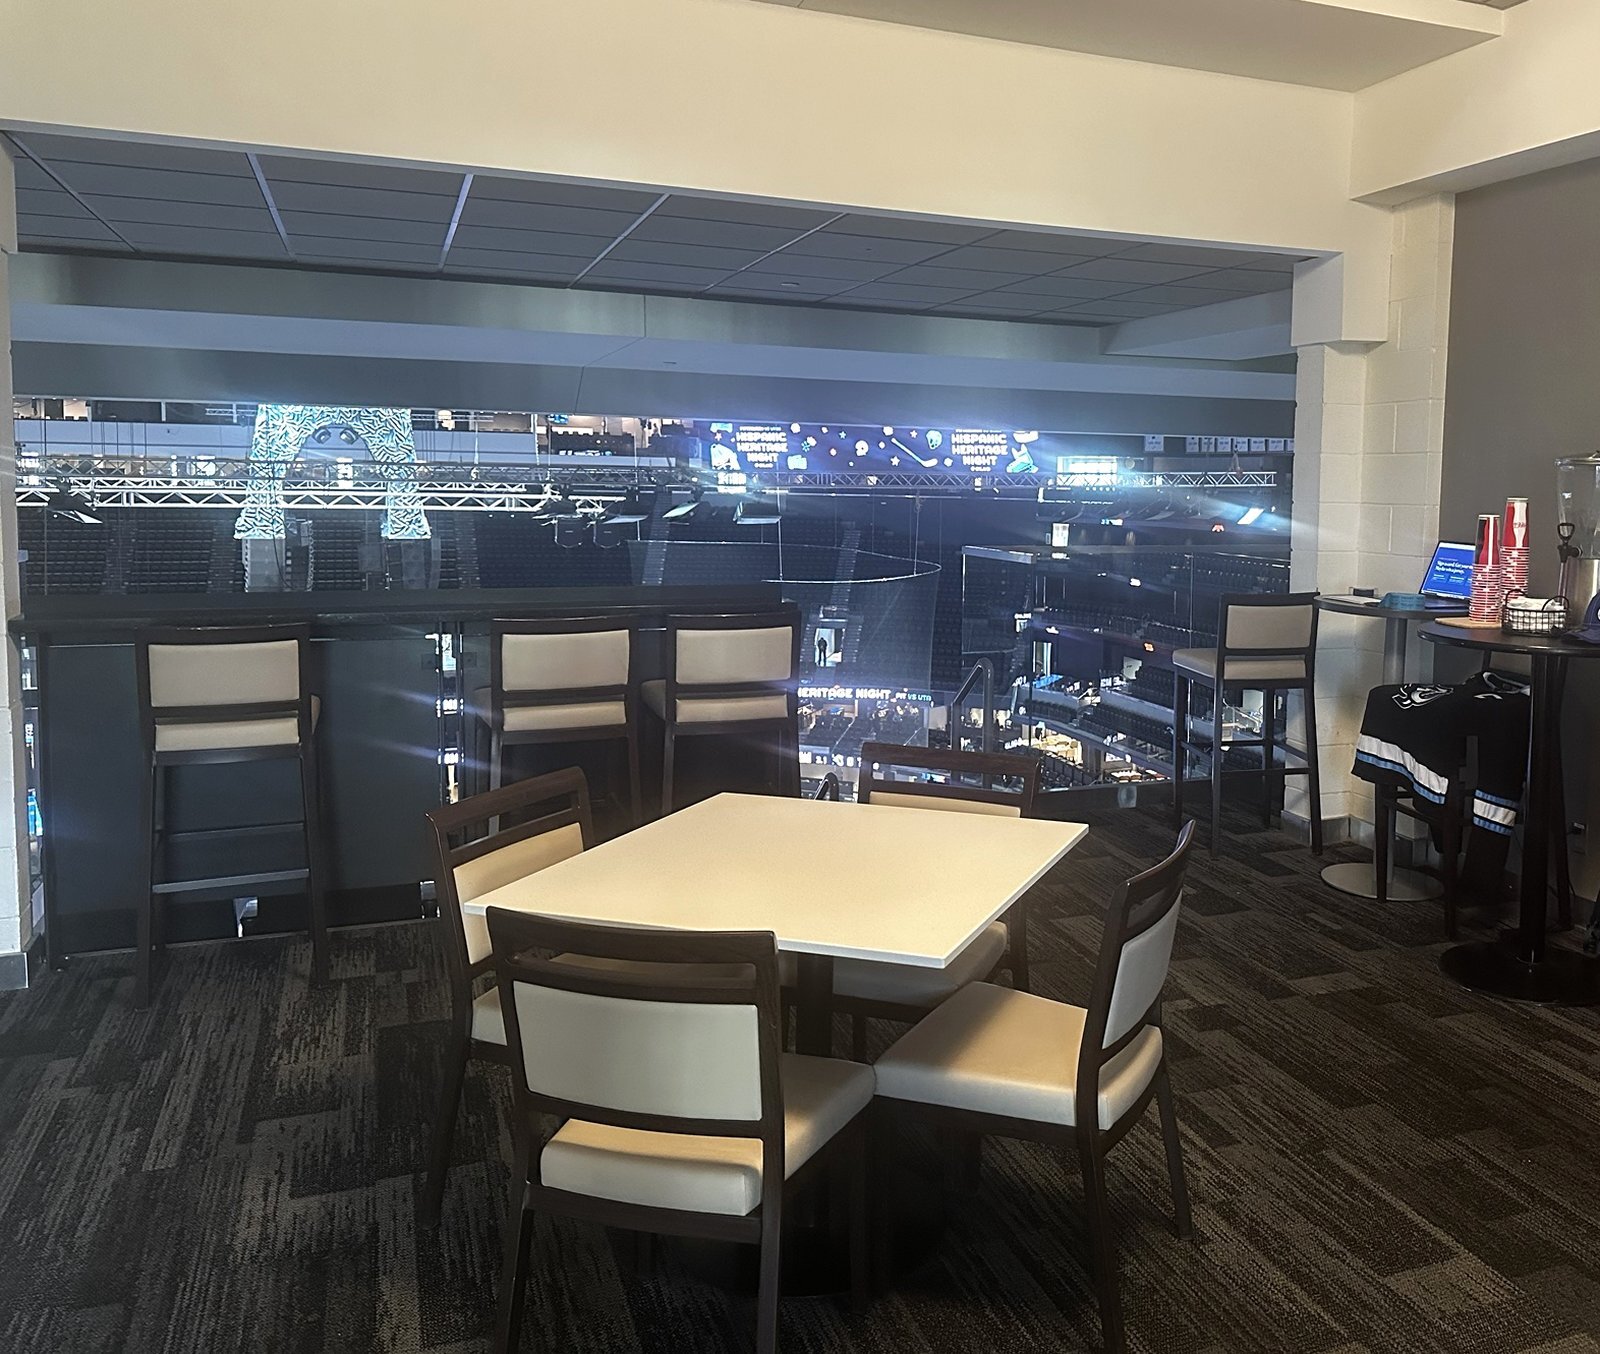
The line item nobody thinks they control
Cyber insurance premiums have gone one direction for five years. Most companies treat the renewal like weather: it arrives, it’s worse than last year, you pay it. What underwriters don’t advertise is that they’re pricing risk, and the same handful of controls that reduce your risk reduce your price. Organizations running a NIST-aligned security stack are seeing premiums 20–30% below the standard market rate — often enough to pay for the upgrades that earned the discount.
Six things that actually move the number
You could fill out a 40-page application and still not know which answers matter. These are the ones that do:
- MFA on everything — email, VPN, admin accounts, 95% of users or better.
- Something watching every endpoint, and someone watching the something.
- Backups that ransomware can’t reach: off-site, immutable, tested.
- Patched and hardened: no open RDP, no legacy SMB, a Microsoft Secure Score you’d show someone.
- People who know: phishing training, and a wire-transfer rule that requires two humans.
- An incident response plan that exists on paper before the incident.
If you can say yes to all six and prove it, you’re already paying too much.
The part that matters at claim time
Here’s the piece we spent the most time on. Claims get reduced or denied when the controls on the insurance application don’t match what’s actually running on the day of the breach. Someone filled out the form from memory eighteen months ago; something changed; nobody updated anything. The policy was only ever worth what it would pay, and now it pays less.
That’s why we built our managed security service to monitor the environment against the policy’s requirements for the whole term — not just to get you the discount, but to keep you the company the underwriter thought they insured.
How to find out your number
Through our partnership with SeedPod Cyber, we offer a free assessment: a read-only scan of your Microsoft 365 tenant, a few questions the scan can’t answer, and two quotes back — your rate as you are, and your rate with the gaps closed — plus a roadmap for closing them. No application. You can bind, take it to your broker, or just keep the roadmap.
For anyone who was in the suite, or wishes they had been: every assessment completed by November 20 is an entry to win a Utah Mammoth jersey signed by Clayton Keller and a puck signed by Gavin McKenna, last year’s No. 1 overall pick. Email Shea or Brent at shea.taylor@ostailors.com or call 801-218-3354 and we’ll send you the link.
Thanks to everyone who braved the traffic. The Mammoth won. So did the people who signed a card.
Insurance is quoted and bound by SeedPod Cyber, LLC. Open Source Tailors provides the security assessment. One drawing entry per organization; public-sector guests receive a charitable donation of equal value in place of a prize.